 Cerberus
 PHP initiative: a free PHP2Shell check for everyone
This is a special initiative to help secure the world. What is happening with PHP2Shell is a disaster, and we are seeing the evidence of the chaos. PHP2Shell (CVE-2026-109618 and CVE-2026-109619) can allow remote code execution without authentication. To battle it, everyone gets a free security check to find out whether they are vulnerable.
: a quick recap
This is a disaster. Almost all companies running PHP are at the highest risk.
What it is
Two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on the CVSS scale. They can let an attacker run code on your server without logging in.
How it works
One bug triggers when PHP runs out of memory partway through setting up a request, and the cleanup code trusts half-built data. The other leaves internal state pointing at memory that no longer exists, so the next request handled by the same worker can act on leftovers.
What happened
Every setup that serves web requests is affected, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. The details leaked before the planned disclosure, so patches were released a day early.
To battle this, we are launching the Cerberus PHP initiative
Everyone gets a free security check to find out whether they are vulnerable to PHP2Shell. Apply below, verify your domain, and Cerberus runs the check.
Three steps to know if you are vulnerable
Fill out the form
Tell us about your company and the domain you want checked.
Verify your domain
We confirm that you own the domain before any check starts.
Get your free security check
Cerberus checks whether you are vulnerable to and we send you the result.
Meet Cerberus
We built the world's first technology that uses mathematics to restrict AI and guarantee that it won't escape the approved scope of actions and can't act on hallucinations during cybersecurity operations, solving the jailbreak problem.
We applied it and created the first AI hacker that you can trust: you don't have to worry that it will hallucinate and drop your database, and you can trust it with your vulnerabilities.
Why you need an AI hacker
Every week another company gets breached. The standard answer — a manual pentest from a consultancy — costs $80k–$200k, takes six weeks, covers 5% of your surface area, and happens twice a year. Between those two snapshots you are flying blind.
An AI hacker changes the math. Continuous testing, every day, across everything you own. That's not an efficiency gain. That's a different category of defense. The only question left is: can you actually trust one near your production systems?
100% control.
You are not handing the keys to a black box.
Attestable
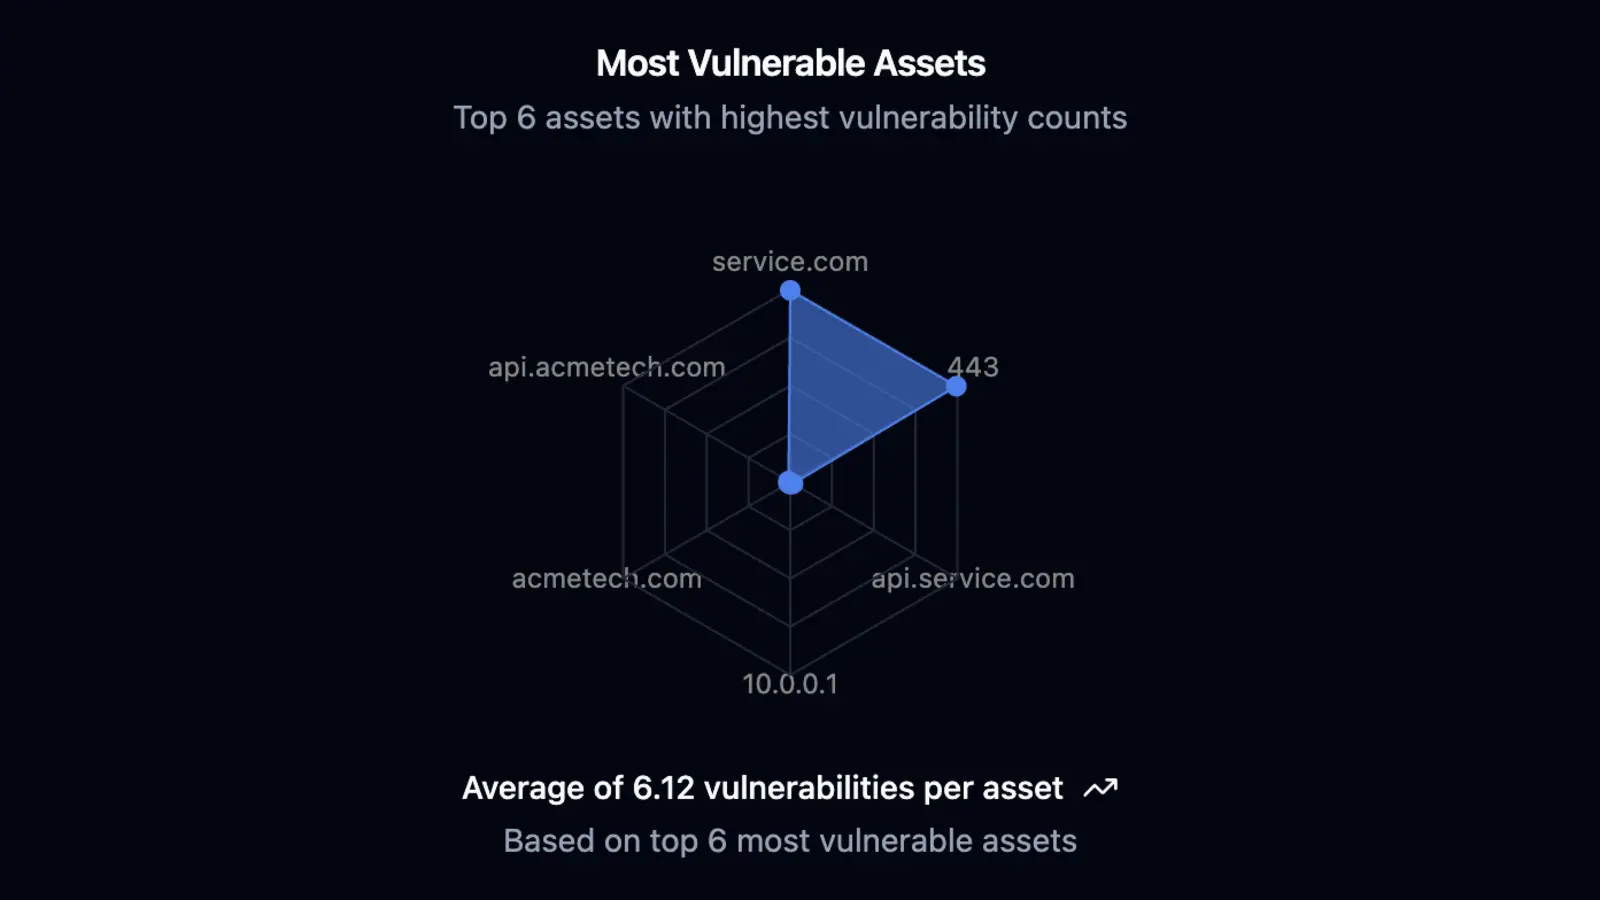
Every action is auditor-ready. Proof artifacts for every command executed.
Interruptible
Pause, redirect, or take manual control at any point in the collaborative environment.
Enforced
Scope is enforced by the compiler, not a policy PDF. You are relying on mathematics.
Backed by real research
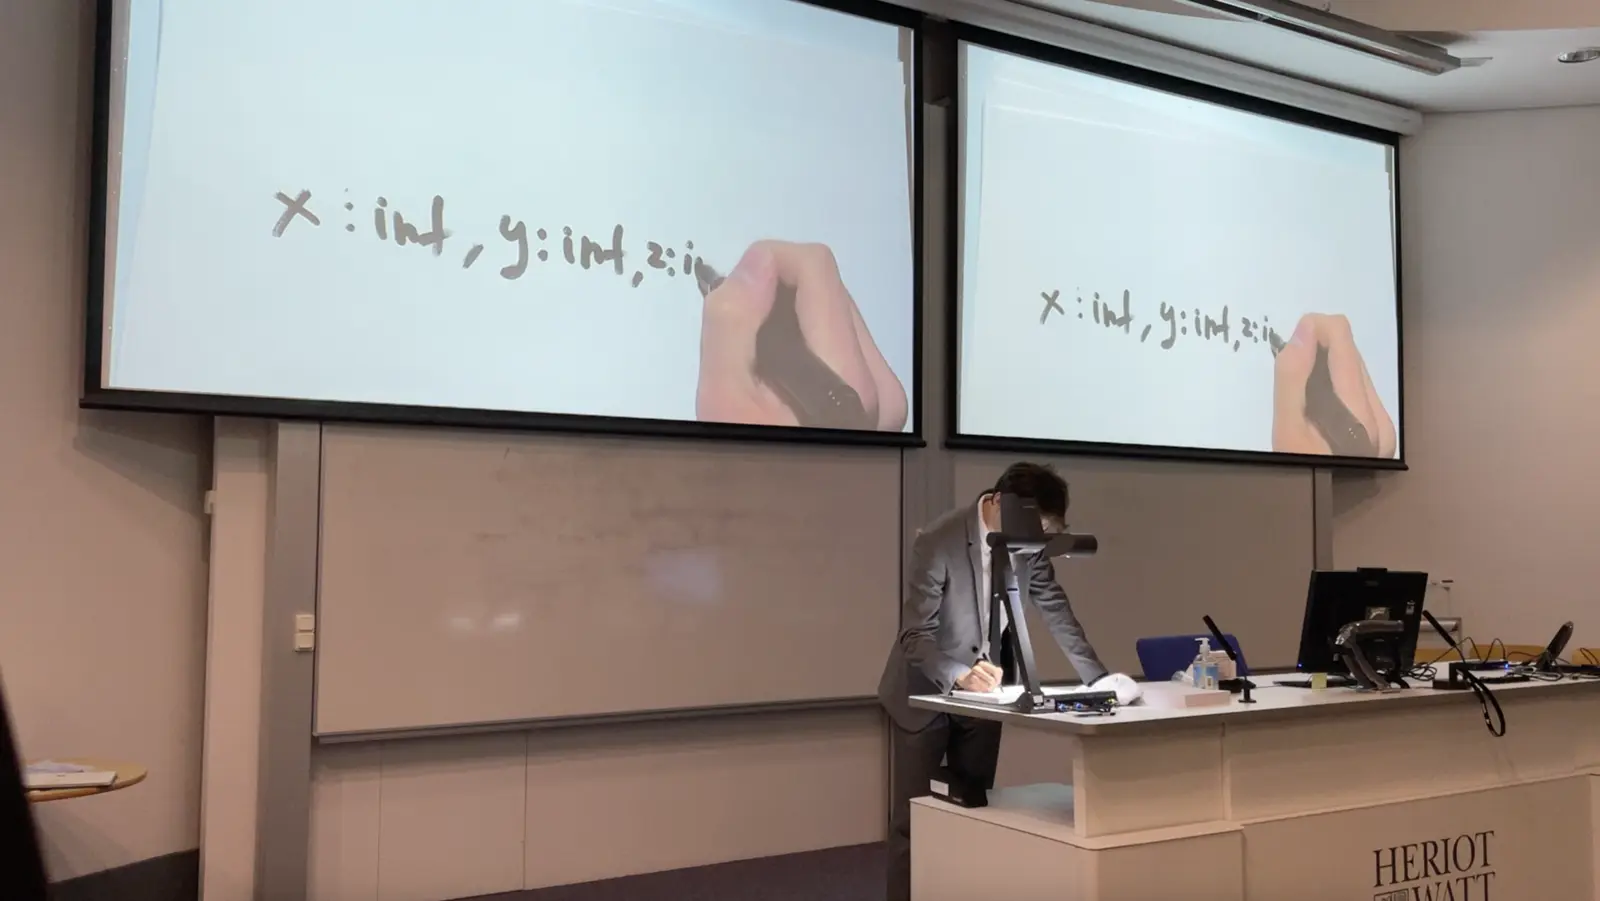
This isn't a marketing claim dressed up in math vocabulary. Cerberus Lang and the proof-carrying execution model are grounded in original research in type theory and formal verification — the kind of work that has to be published, peer-reviewed, and reproduced.
No other AI pentest vendor has this background on their team. It is the reason we can ship what we ship.

Apply for your free check
Fill out the form below. You will be asked to verify your domain, then we run the check and send you the result.